United Airlines Bans AI Booking Agents: A Security Wake-Up Call for Support Automation
In a landmark move that has sent ripples through the travel tech and customer support industries, United Airlines announced it will prohibit the use of personal AI assistants to book flights, change reservations, or access its systems. The decision, framed as a necessary protection of consumer privacy and aviation security, draws a hard line in the sand between enterprise-grade automation and the unbridled use of third-party bots.
While consumers have embraced AI to streamline tasks, from ordering groceries to managing calendars, United’s crackdown reveals the fragile tension between convenience and compliance. For B2B SaaS leaders, support team managers, and operations specialists, this isn't just an aviation headline. It’s a critical case study on the infrastructure risks of shadow AI and a guidepost for building secure, scalable support automation that won’t get your users banned.
Why United Drew a Line in the Silicon Sand
On November 12, 2026, United Airlines clarified that it will not allow third-party AI agents (often called 'personal AI assistants') to engage with its digital infrastructure. This isn't merely a UX preference; it's a multi-layered liability decision grounded in regulatory exposure, data sovereignty, and operational integrity.
The Regulatory Tripwire: ACAA and the Human-in-the-Loop Mandate
One of the most immediate triggers for the ban is the legal requirement under the Air Carrier Access Act (ACAA) and related federal regulations. At the check-in flow, human passengers must explicitly verify that their bags do not contain hazardous materials, including lithium batteries with specific charges.
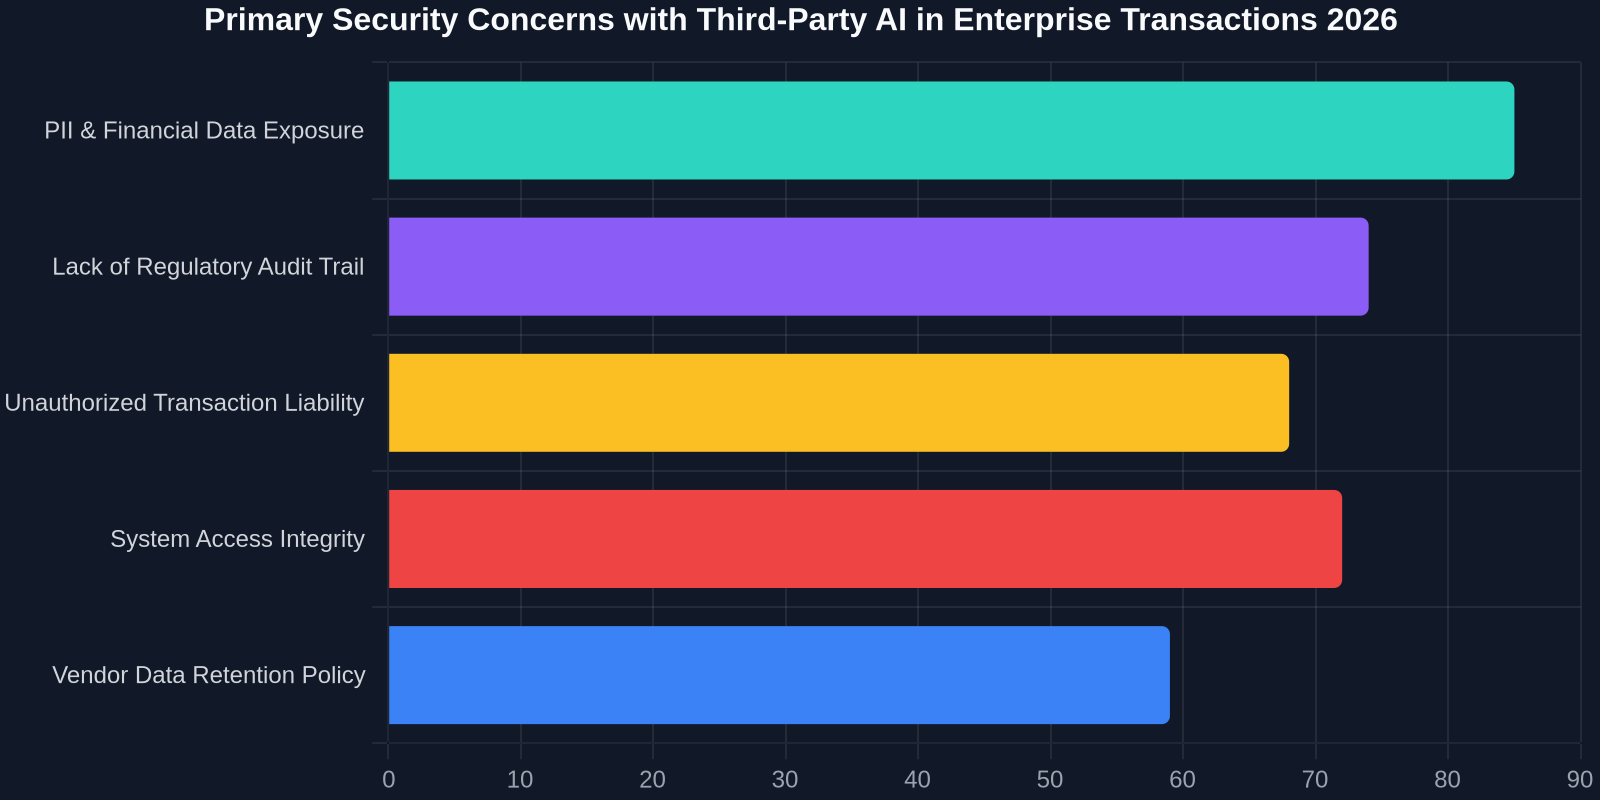
United says automated actions could violate aviation regulations, citing the requirement for a human acknowledgment during check-in that bags contain no banned items. If an unsupervised AI agent clicks the "I agree" checkbox for a passenger, the airline is potentially exposed to severe fines, cargo fires, and legal nightmares. Support leaders managing compliance-heavy industries (healthcare, finance, logistics) recognize this friction immediately: automation without verified identity and explicit consent is a non-starter.
Data Security: Who Owns Your Passport Details Now?
The airline says customers who give their personal and credit card information to AI businesses run the risk of having their sensitive data exposed. When a traveler hands over their PNR (Passenger Name Record), passport number, and credit card CVV to a consumer LLM wrapper, that data usually leaves the secure envelope of the airline’s infrastructure. Unlike PCI-DSS compliant enterprise tools, most personal AI agents operate in a black-box environment where data may be retained, used for model training, or exposed to third-party APIs.
The Hidden Cost of 'Convenience': Fragmented Record-Keeping
Imagine a support ops nightmare: a traveler's AI agent changes a flight segment overnight, but the passenger isn't aware. They show up at the gate, and the ticket is voided due to a fare rule miscalculation by the bot. Who is liable? The agent developer? The LLM provider? The passenger?
The customer experience liability of ungoverned AI isn't a hypothetical. It's a 'ticking time bomb' for support operations where agents act without a comprehensive source of truth.
United has said it will not cancel reservations made by AI agents before November 11, 2026, a grandfathering grace period. However, post-crackdown, any third-party bot attempting to scrape fares, manipulate PNRs, or trigger automated check-ins will be formally blocked. For support teams, this underscores a critical truth: automation without bi-directional system integration and pristine data hygiene is a revenue risk, not a timesaver.
Implications for Customer Success and Support Operations
United Airlines CEO Scott Kirby is hyperfocused on improving the flying experience, and this policy enforcement is a trust-building exercise, not an anti-AI Luddite move. It differentiates between 'authorized interfaces' (direct airline apps, trusted travel management company integrations) and 'rogue automation.'
For support leaders scaling B2B operations beyond just travel, every ticket created by a hallucinating AI erodes trust in the automation pipeline. The United ban teaches us three architectural imperatives for secure support automation:
- Channel Sanctioning: Automate where you control the interface. Public-facing, unauthenticated bot traffic is a security hole. Proactive support must operate within a managed context.
- PII Hygiene at the Kernel Level: You cannot feed raw, unmasked payment card data or identity documents into a generalized, third-party model. AI-native support platforms must ensure zero retention of sensitive identity artifacts.
- Human-on-the-Loop for Critical State Changes: In finance, travel, or medical scheduling, an automated resolution should still generate a verifiable human sign-off for high-stakes finalization (e.g., a wallet charge, a seat upgrade, a prescription refill).
Data Sovereignty in the Age of Agentic Flows
United Airlines is restricting artificial intelligence agents from booking flights for travelers, but they aren't killing AI. They are implicitly demanding a shift to private, enterprise-grade AI where data sovereignty is guaranteed. When a business leverages a platform like Successly for customer automation, the AI isn't a random internet scraper; it operates under a strict data processing agreement (DPA) and within a shielded namespace.
The 'Shadow AI' Risk Matrix for Support Functions
When a support agent connects their work console to a consumer AI to 'automate' ticket summaries, they inadvertently export internal knowledge base articles, customer emails, and performance metrics. United Airlines is blocking third-party AI assistants from booking flights to protect payload data; enterprises should apply the same firewall to their ticket management systems to protect IP.
| Security Dimension | General Personal AI Agent | Managed Enterprise Support AI |
|---|---|---|
| Data Residency | Retained for training | Isolated, zero-retention |
| Regulatory Compliance | No audit trail | ACAA/GDPR-ready logs |
| Purchase Authorization | Proxy credentials | Tokenized, verified actions |
| Liability Chain | Fragmented (user ↔ bot ↔ API) | Unified vendor accountability |
The Future of Travel (and Support) is Verified Automation
The airline industry is a bellwether for digital transformation. Today it's the booking engine; tomorrow it's the medical claim processor or the mortgage underwriter. The announcement that travelers who previously used AI assistants to book flights are on borrowed time isn't a tech rejection. It's a pivot toward Verified AI Workflows.
Por qué los usuarios de Successly evitan la trampa de la 'Prohibición de United'
Las plataformas diseñadas para el éxito del cliente empresarial (no para la conveniencia del consumidor) diseñan resultados deterministas y no alucinatorios. En lugar de otorgar acceso sin restricciones a la API a un LLM errante, una IA enfocada en soporte utiliza clasificación de intenciones para seleccionar un endpoint de API seguro, autentica la sesión del usuario y crea un artefacto de interacción completamente registrado.
Esto garantiza que los check-ins automatizados, reembolsos o cambios de cuenta cumplan con las regulaciones específicas de la industria y no resulten en una lista negra pública por parte de un proveedor de servicios importante. En un panorama donde United está diciendo 'no' a agentes no verificados, el mercado clama por soluciones de automatización B2B que puedan decir 'sí, de forma segura'.
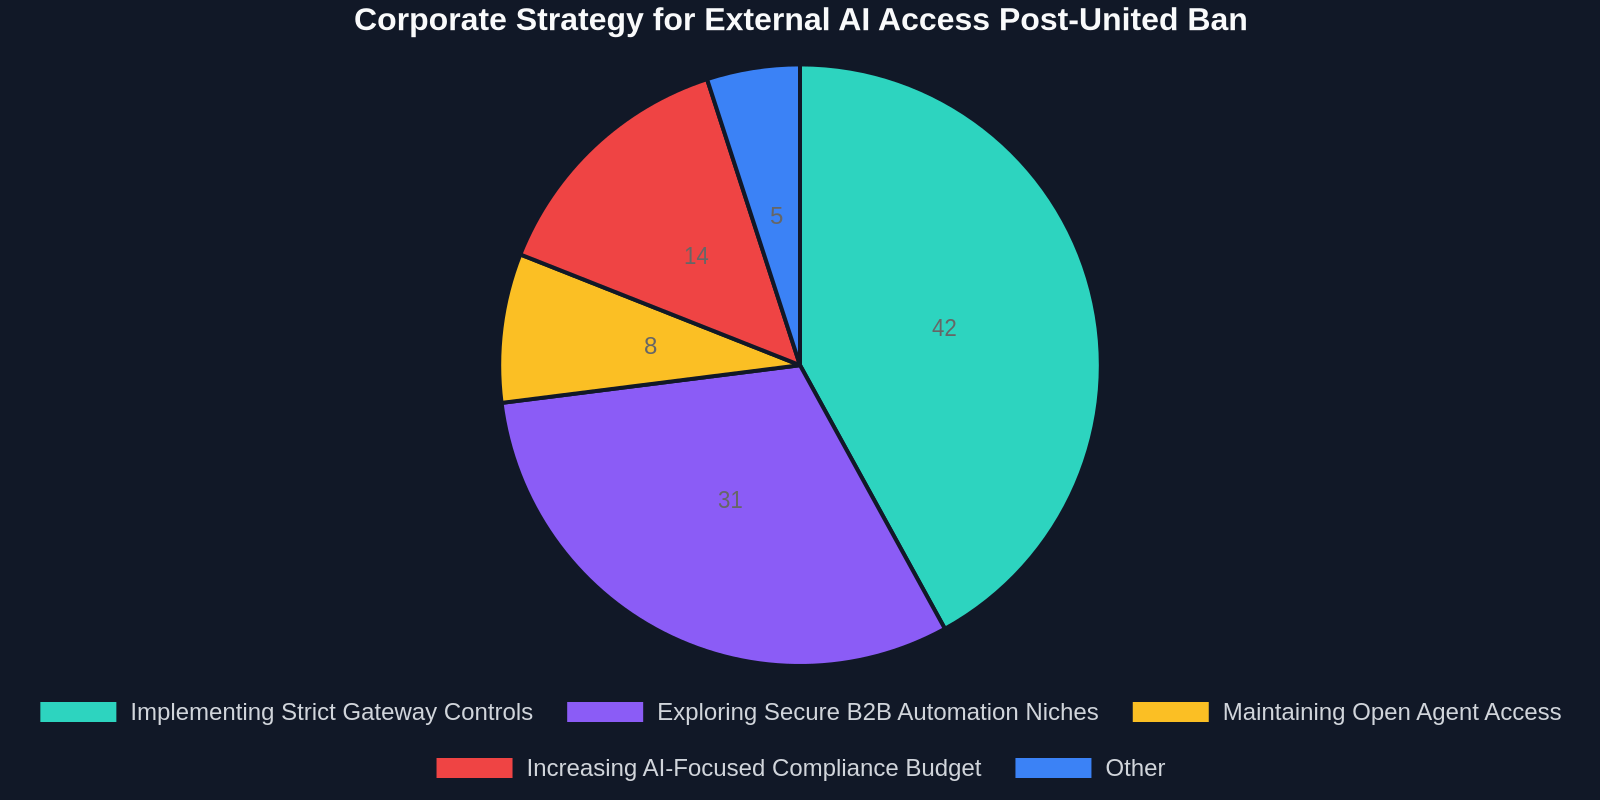
Construyendo un Plan de Automatización Segura: Lista de Verificación para Líderes de Soporte
Para evitar la fragmentación que desencadenó la suspensión de United, los líderes de soporte deben pasar del bloqueo reactivo de bots al diseño de arquitectura robusta. Aquí hay una lista de verificación de preparación para la automatización derivada directamente del incidente de United:
- Implementar Vinculación de Identidad de Confianza Cero: Los agentes nunca deben depender de claves API en texto plano extraídas por una extensión de navegador. Utilice OAuth 2.0 con acceso de cliente tokenizado.
- Exigir Confirmación de Acción para Eventos de Alto Riesgo: Una transacción monetaria o un cambio de vuelo debe activar una confirmación push explícita al dispositivo verificado del usuario.
- Restricción de Protocolo: Rechace la automatización masiva a través de canales no oficiales. Utilice middleware de soporte dedicado que imponga limitación de velocidad y enmascaramiento de datos.
Conclusión: El Foso de la IA es la Confianza
La prohibición de asistentes personales de IA por parte de United Airlines es la corrección del mercado de una suposición peligrosa: que la inteligencia pública y multiinquilino es segura para transacciones privadas. Para fundadores de SaaS, VP de éxito del cliente y directores de operaciones de soporte, la lección es clara: el futuro no se trata de bloquear la IA; se trata de implementar IA detrás de una señal segura.
La automatización falla cuando erosiona el límite de cumplimiento entre el proveedor de servicios y el usuario final. La marca que resuelva esta brecha de confianza se volverá indispensable.
A medida que la industria se solidifica en carriles de 'IA confiable' e 'IA rogue', asegúrese de que su stack de soporte esté en el primero. Invierta en automatización que respete la residencia de datos, defina una responsabilidad legal clara y mantenga el reconocimiento de humano en el circuito donde la ley lo exija. Porque el ticket de soporte más caro no es el que resuelve con IA, sino el que una IA rogue crea.